
OSINT
FOR MODERN INVESTIGATIONS
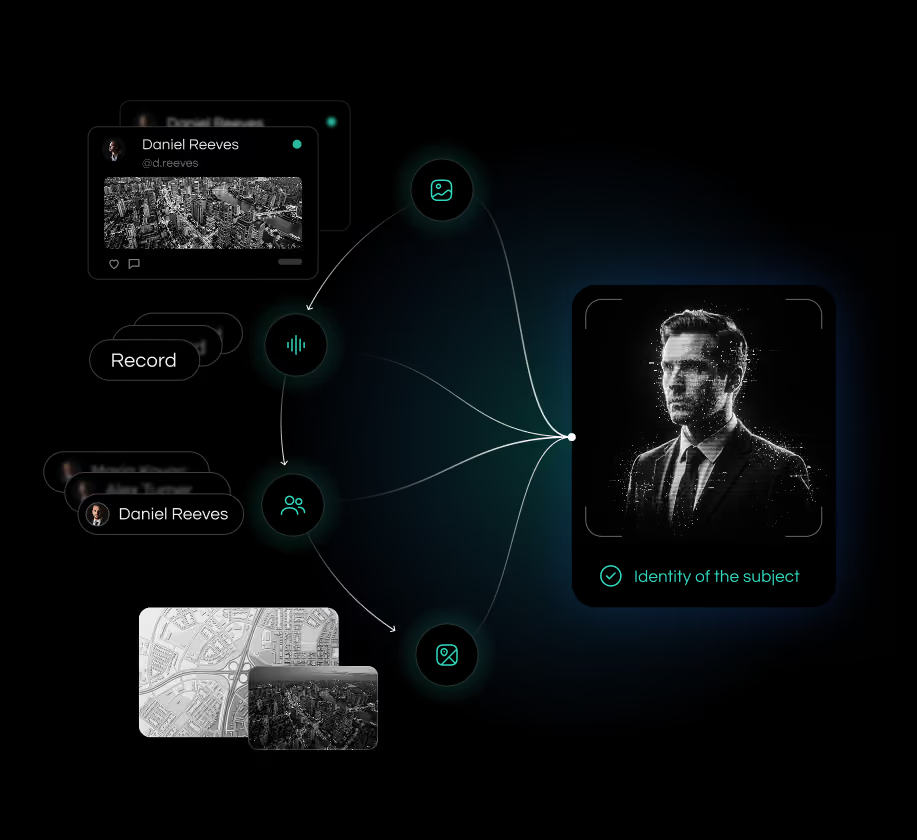

OSINT turns publicly and commercially available information into verified, actionable intelligence. See how professional teams move from an investigation question to a defensible answer—and where Social Links solutions fit.
Built for law enforcement, national security, cybersecurity, corporate intelligence, due diligence, and professional investigations.
SOCIAL LINKS IN NUMBERS
500+
Sources available in SL Crimewall
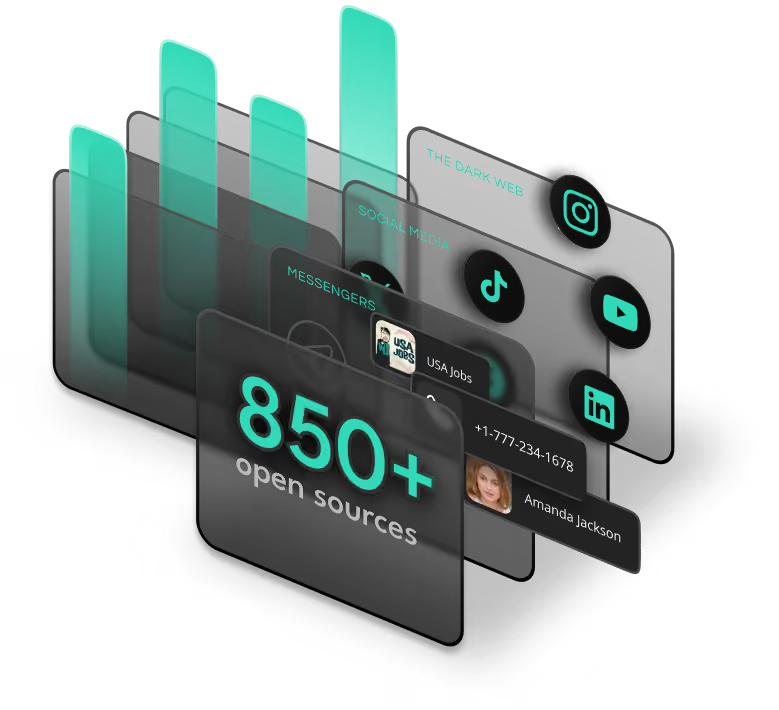
850+
Open-source feeds available through SL API
80+
Countries where teams rely on Social Links solutions
4 PATHS
Workspace, API, Maltego, or private deployment
Product facts checked against current Social Links product documentation. Methodology references include ODNI, OHCHR, and ICO guidance. Last reviewed October 2026.
ONE INTELLIGENCE CYCLE.
SIX CONNECTED STAGES.
Select a stage to see how disciplined investigations move from a question to a reviewable intelligence product.
Turn a broad concern into a precise, lawful, answerable question. Set scope, priority, timeframe, jurisdiction, confidence threshold, and decision owner before collection begins.
Input
Business or investigative question
Control
Authority, scope, and minimization
Output
Collection plan and success criteria
Select source categories that can answer the requirement. Capture provenance, timestamps, access conditions, and context while avoiding unnecessary collection.
Input
Approved collection plan
Control
Access, necessity, and provenance
Output
Relevant source material
Normalize records, extract identifiers, remove duplicates, and connect people, organizations, infrastructure, places, wallets, events, and digital artifacts.
Input
Heterogeneous source data
Control
Normalization and entity rules
Output
Structured entities and relationships
Corroborate critical facts across independent sources. Check dates, origin, ownership, manipulation risk, alternative explanations, and information gaps.
Input
Candidate findings
Control
Source quality and corroboration
Output
Confidence-rated facts
Interpret verified relationships in context. Build timelines, test hypotheses, assess competing explanations, identify gaps, and connect evidence to the decision.
Input
Verified facts and relationships
Control
Analytic standards and peer review
Output
Defensible intelligence assessment
Deliver a concise assessment with evidence, limitations, confidence, and recommended actions. Preserve the audit trail and monitor for material change.
Input
Intelligence assessment
Control
Review, retention, and dissemination
Output
Decision, case package, or alert
ONE INTELLIGENCE CYCLE.
SIX CONNECTED STAGES.
Select a stage to see how disciplined investigations move from a question to a reviewable intelligence product.
Turn a broad concern into a precise, lawful, answerable question. Set scope, priority, timeframe, jurisdiction, confidence threshold, and decision owner before collection begins.
Input
Business or investigative question
Control
Authority, scope, and minimization
Output
Collection plan and success criteria
Select source categories that can answer the requirement. Capture provenance, timestamps, access conditions, and context while avoiding unnecessary collection.
Input
Approved collection plan
Control
Access, necessity, and provenance
Output
Relevant source material
Normalize records, extract identifiers, remove duplicates, and connect people, organizations, infrastructure, places, wallets, events, and digital artifacts.
Input
Heterogeneous source data
Control
Normalization and entity rules
Output
Structured entities and relationships
Corroborate critical facts across independent sources. Check dates, origin, ownership, manipulation risk, alternative explanations, and information gaps.
Input
Candidate findings
Control
Source quality and corroboration
Output
Confidence-rated facts
Interpret verified relationships in context. Build timelines, test hypotheses, assess competing explanations, identify gaps, and connect evidence to the decision.
Input
Verified facts and relationships
Control
Analytic standards and peer review
Output
Defensible intelligence assessment
Deliver a concise assessment with evidence, limitations, confidence, and recommended actions. Preserve the audit trail and monitor for material change.
Input
Intelligence assessment
Control
Review, retention, and dissemination
Output
Decision, case package, or alert
DATA FROM ALL SOURCES,
IN ONE PLACE
Source breadth increases discovery. Independent corroboration, provenance, timing, and context increase confidence.
MEDIA
Profiles, posts, connections, media, communities, and behavioral signals.
INFRASTRUCTURE
Domains, DNS, certificates, IPs, websites, archives, and technical artifacts.
RECORDS
Corporate registries, filings, court records, sanctions, and official datasets.
WEB
Forums, marketplaces, leak sites, paste services, and threat-actor mentions.
BLOCKCHAINS
Wallets, transfers, counterparties, transaction patterns, and attribution clues.
DATA
Credential exposures, malware logs, historical leaks, and identity pivots.
MEDIA & DOCUMENTS
News, images, video, metadata, reports, publications, and geospatial evidence.
COMMERCIAL DATA
Licensed datasets and enrichment sources available under defined terms.
INTERNAL DATA
Customer, case, threat, and proprietary records combined in controlled environments.
Collection is not
the finish line
Record source and observation time
Separate originals from reposts
Preserve context and limitations
Apply authority and minimization rules
DIFFERENT MISSIONS.
THE SAME NEED FOR EVIDENCE.
Select a mission to see the question, signals, and intelligence output that matter most.
Connect identities, events, and networks
Typical question
Which entities and digital assets are connected to the subject?
Intelligence output
Entity graph, timeline, evidence package, and lead assessment.
01
Identity & aliases
Resolve
02
Social & messaging footprint
Map
03
Events, places & media
Correlate
04
Independent source checks
Verify
05
Lead & evidence report
Deliver
Profile actors, infrastructure, and exposure
Typical question
What is the actor’s infrastructure, capability, and exposure to us?
Intelligence output
Actor profile, infrastructure map, indicators, and monitoring plan.
01
Handles & aliases
Identify
02
Domains, IPs & certificates
Map
03
Leaks, forums & malware
Correlate
04
Infrastructure history
Verify
05
Indicators & watchlist
Operationalize
Detect fraud, impersonation, and hidden risk
Typical question
Is this identity, transaction, vendor, or digital asset trustworthy?
Intelligence output
Risk assessment, relationship map, evidence summary, and escalation path.
01
Identity attributes
Enrich
02
Corporate & social links
Connect
03
Behavioral signals
Detect
04
Independent evidence
Validate
05
Risk recommendation
Decide
Understand people, companies, and counterparties
Typical question
What material facts or relationships could change the decision?
Intelligence output
Subject profile, red flags, source appendix, and confidence-rated assessment.
01
Corporate records
Establish
02
Public footprint
Review
03
Associations & exposure
Connect
04
Adverse findings
Corroborate
05
Decision brief
Deliver
DATA BECOMES INTELLIGENCE WHEN IT ANSWERS A QUESTION
The right solution depends on where analysts work, how data enters the investigation, and what deployment controls your organization requires.
FULL-CYCLE WORKSPACE
SL CRIMEWALL
Collect, analyze, visualize, monitor, collaborate, and report in one investigation platform. Best for teams that need an end-to-end OSINT workspace.
500+ sources
Graph, table & map
SaaS, self-hosted, on-prem
DATA INFRASTRUCTURE
SL API
Bring structured, real-time open-source data into internal platforms, enrichment pipelines, fraud systems, and automated workflows.
850+ sources
Real-time data
Built for integration
MALTEGO-NATIVE
SL PROFESSIONAL
Run Social Links transforms and investigation methods inside Maltego for identity, social, darknet, infrastructure, and link analysis.
1,000+ methods
1.3B indexed identities
Maltego integration
CONTROLLED ENVIRONMENT
SL PRIVATE PLATFORM
Combine open-source, third-party, and proprietary data in a customized on-premises environment with organization-specific controls and methods.
On-premises
Private data
Custom methods
FIND THE RIGHT SOCIAL LINKS SOLUTION
Need
Solution
What it gives
Deployment
RUN COMPLETE INVESTIGATIONS
Solution
SL Crimewall
What it gives
Collection, analysis, visualization, monitoring, collaboration, and reporting
Deployment
SaaS, self-hosted, or on-premises
INTEGRATE OSINT DATA
Solution
SL API
What it gives
Structured, real-time data for internal products and automated workflows
Deployment
API integration
INVESTIGATE IN MALTEGO
Solution
SL Professional
What it gives
Social Links methods and live data inside a familiar graph workflow
Deployment
Maltego
CONTROL DATA AND DEPLOYMENT
Solution
SL Private Platform
What it gives
Open, third-party, and proprietary data in a customized private environment
Deployment
On-premises
FOUR INVESTIGATIONS. ONE REPEATABLE METHOD.
The Social Links OSINT Case Book follows four investigations that begin with limited information and expand through identity enrichment, cross-platform pivots, relationship mapping, content analysis, and verification.

CROSS-BORDER SUBJECT PROFILING
Enrich an initial identifier, validate identity, and connect activity across sources and jurisdictions.

CYBER ACTOR PROFILING
Map aliases, infrastructure, activity, and digital relationships around a suspected threat actor.

ORGANIZATIONAL DATA EXPOSURE
Trace leaked information and darknet presence to understand external exposure and response priorities.

CONFLICT-RELATED NETWORK ANALYSIS
Connect identities, content, affiliations, and events to build a reviewable intelligence picture.


CAPABILITY MUST BE MATCHED BY GOVERNANCE
Professional OSINT work needs documented authority, proportionate collection, verifiable sources, secure handling, and human judgment.
01
LAWFUL PURPOSE
Confirm authority, jurisdiction, terms, and organizational policy.
02
NECESSITY & MINIMIZATION
Collect only what is relevant to the defined requirement.
03
PROVENANCE
Preserve source, time, method, context, and analyst reasoning.
04
HUMAN VALIDATION
Use automation as support; analysts own verification and conclusions.
Build methods on accountable standards
Use official guidance to shape policy, training, documentation, and review.
GO DEEPER WITH FOCUSED GUIDES AND RESEARCH
Use this page for the strategic overview. Use dedicated guides for definitions, frameworks, methods, tools, and industry research.
What is OSINT?
A foundational explanation for readers learning the discipline.
Guide
How to structure an OSINT investigation
Process, planning, collection, and analysis.
Framework
Social media intelligence toolkit
Focused workflows and source considerations for SOCMINT.
Methods
OSINT for cybercrime investigations
Threat intelligence, exposure, incident response, and attribution.
Use case
Reports, webinars, and OSINT research
Original research and practical resources from Social Links.
Research
Questions teams ask before operationalizing OSINT
What is OSINT?
OSINT, or open-source intelligence, is intelligence derived from publicly or commercially available information to address a specific requirement. The defining step is verifying, analyzing, and communicating relevant data as a decision-relevant assessment.
How is information different from intelligence?
Open-source information is raw material: records, posts, domains, images, and documents. Open-source intelligence is the assessed output produced after relevant information has been collected, verified, contextualized, and tied to a defined question.
Which sources are used in OSINT investigations?
Depending on the requirement and legal authority, investigators may use social platforms, websites, public records, corporate registries, news, technical infrastructure, blockchain data, leaked datasets, dark-web sources, commercial datasets, and approved internal data.
Is OSINT legal?
Availability does not remove legal, contractual, privacy, or ethical obligations. Teams must consider purpose, jurisdiction, authorization, access terms, necessity, minimization, retention, and secure handling.
How do teams verify OSINT findings?
Analysts corroborate material facts across independent sources, confirm timing and provenance, test alternative explanations, preserve context, document limitations, and separate observed fact from inference.
Which Social Links solution should we choose?
Choose SL Crimewall for an end-to-end investigation workspace, SL API to integrate structured data into your systems, SL Professional to work inside Maltego, or SL Private Platform for a customized on-premises environment.
Can AI automate an OSINT investigation?
AI can accelerate search, extraction, entity resolution, summarization, and prioritization. It should not replace legal review, source evaluation, corroboration, analyst judgment, or accountability for the final assessment.
OSINT solutions
you can trust
Companies from S&P500 and law enforcement agencies from 80+ countries rely on Social Links' solutions.


Digital Investigator
Government
“Absolutely love this tool!
The tool is very easy to use and it works perfect, whenever I would want to see something added a simple mail is enough to make the team work on it.”
Intelligence Analyst
Government
“Very Good Tool For Online Investigations.
Very powerful tool for OSINT investigations. Easy to use and to integrate.”
Digital Investigator
IT
“Social Links experience used for cybercrime investigation
Superb OSINT data source and rich in historical data that can be use in pivoting process and investigation. Helps in my cybercrime investigation and attributing to entities associated with my case.”
Top picks from
our blog


Book your free, personalized demo.
Want to see how Social Links can enhance your OSINT capabilities? Have questions about our products, data access, or pricing? Fill out the form, and our team will get in touch shortly.
With Social Links, you can:


Book your free, personalized demo.
Want to see how Social Links can enhance your OSINT capabilities? Have questions about our products, data access, or pricing? Fill out the form, and our team will get in touch shortly.
With Social Links, you can: